
Blockchain & digital trust
Design the controls around every signature.
Build wallet interfaces and signing workflows around a defined custody and authority model. We address transaction preparation, policy approval, key-system integration and recovery responsibilities as separate engineering decisions.
SEE HOW THE TECHNOLOGY WORKS
A shared record. A clear chain of responsibility.
See where signatures and shared records fit into a real enterprise workflow.
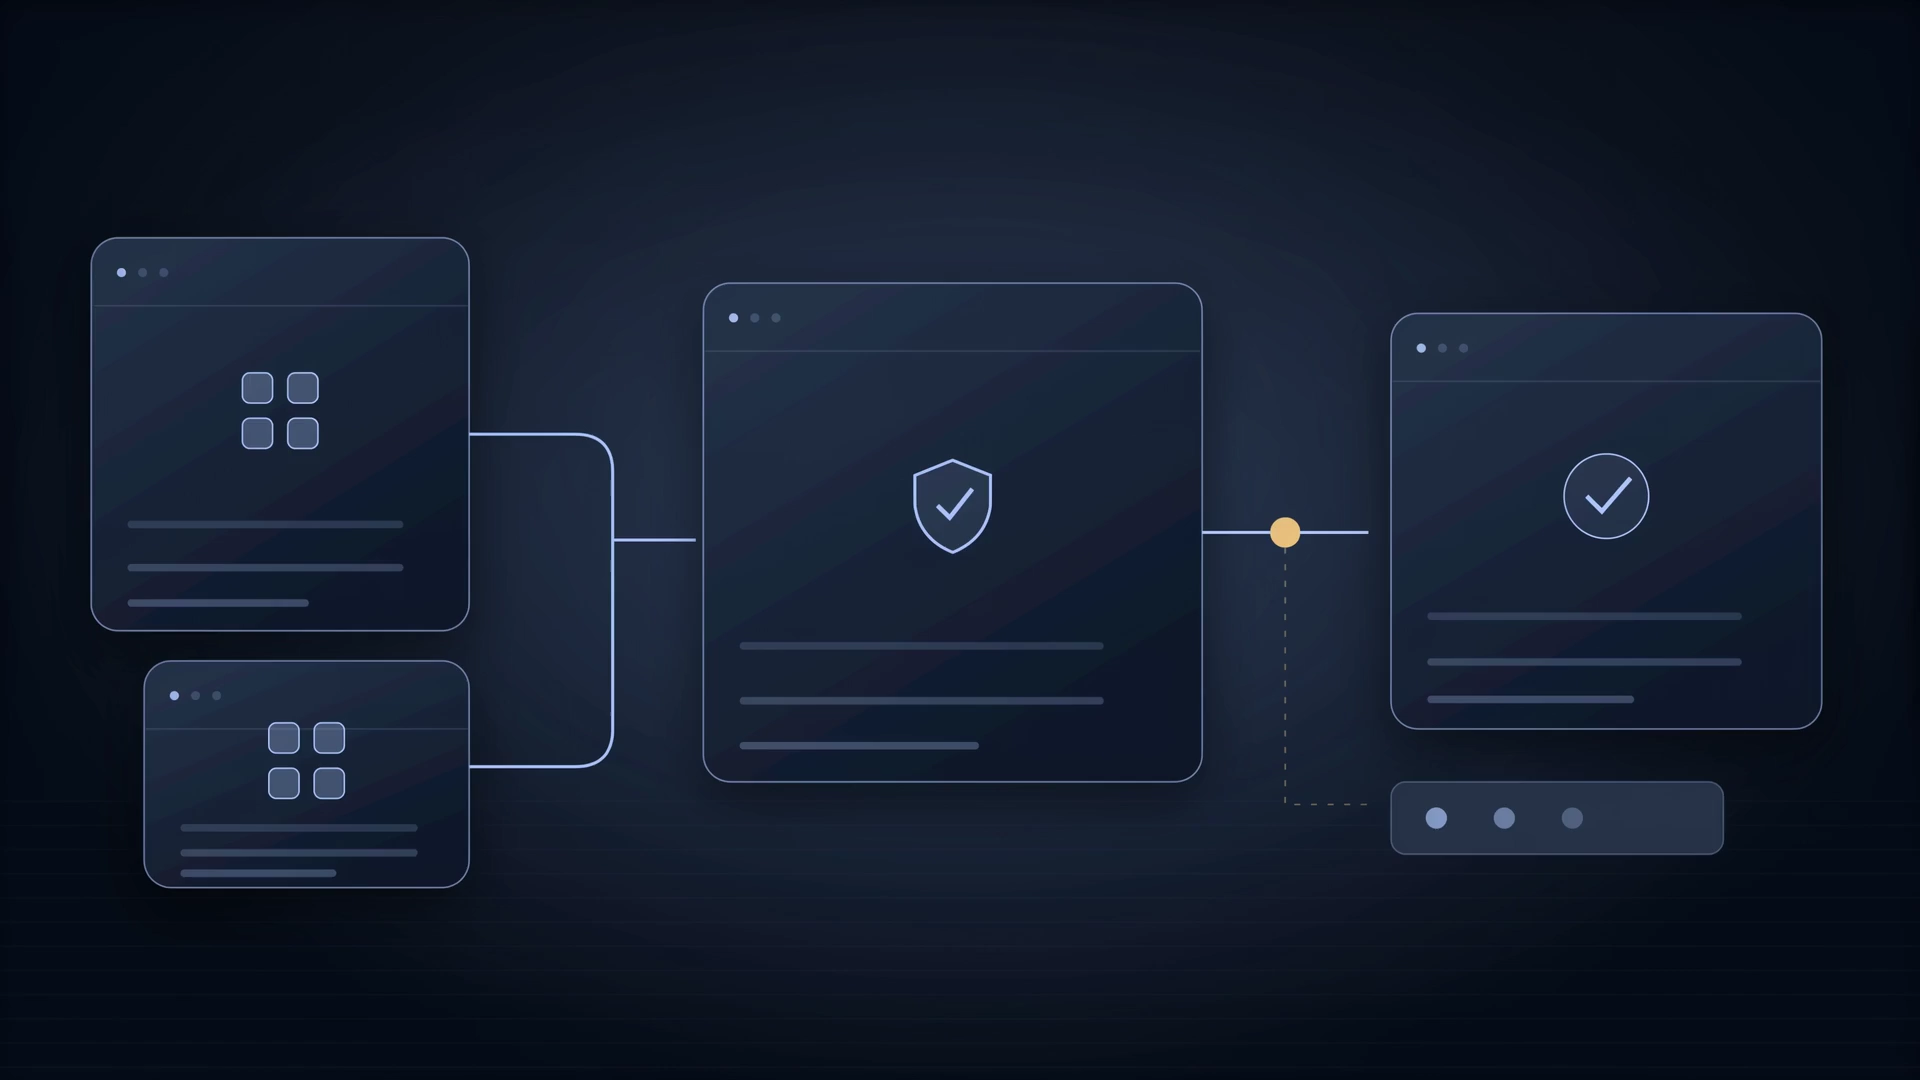
INTERACTIVE WORKFLOWIllustrative engineering scenario
01 / 03
Establish the source
Define who supplies the record, what the source system verifies and who is allowed to sign.
A business record and identified issuerAn authorized signed assertion
Read the complete workflow
Establish the source
Define who supplies the record, what the source system verifies and who is allowed to sign.
A business record and identified issuer → An authorized signed assertion
Coordinate participants
Agree the participant permissions, validation rules and correction process before selecting the network design.
Signed record + network rules → A consistent shared event history
Connect the workflow
Connect records to enterprise systems and make the audit trail inspectable. A ledger records a claim; it does not independently prove the physical event.
Recorded event + integration scope → Traceable system updates
Policy-controlled transaction approvals
Custody-provider and signing-system integration
FROM INPUT TO USEFUL OUTPUT
Follow the work. Inspect the result.
Explore a proposed delivery workflow. Each step connects an activity to something your team can review.
WORKFLOW BLUEPRINTIllustrative delivery design
INPUTS TO DEFINE
Custody provider and authority decisions
Target networks and transaction types
Approval, recovery and operating requirements
REVIEWABLE OUTPUT
A custody and signing responsibility model
Map the account, key and recovery owners. Specify transaction policies, approval thresholds and the systems permitted to request a signature.
Reviewed against agreed requirementsWHAT WE DEFINE AND DELIVER
Practical artifacts. A shared definition of done.
The exact scope follows discovery. These are the building blocks we discuss, specify and review together.
- Custody and authority architecture
- Wallet and transaction interfaces
- Signing-policy and key-system integration
- Recovery and reconciliation workflows
HOW THE PIECES CONNECT
Architecture with your operation in mind.
Application → transaction policy → authorized signing/key service → network submission → indexing and reconciliation. Custody responsibilities are not transferred implicitly by building an interface.
Designed around real constraints.
- Block Gemini is presented here as an engineering provider, not a licensed custodian or guarantor of asset recovery.
- Supported networks, signing methods and recovery options depend on the selected providers and architecture.
FIND THE RIGHT STARTING POINT
A product where it fits. A custom build where it matters.
Decide who controls keys and approvals before designing the transaction experience. The interface must reflect those responsibilities.
Bring your objective and the people it should help. We will shape a first scope and the evidence needed to move forward.
Discuss this projectYour starting point is carried into an editable inquiry. Nothing is booked or provisioned by making this selection.A CLEAR PATH THROUGH DELIVERY
One plan. Visible progress.
A complete build, a focused integration or specialists alongside your team. The engagement follows the scope—not a fixed team template.
- 01
Discover
Define users, the process, constraints and a useful first measure of success.
- 02
Design
Make the interface, architecture, data and integration decisions visible.
- 03
Build & evaluate
Deliver working increments and test the task, permissions and difficult cases.
- 04
Release & evolve
Agree rollout, recovery, handover and the people responsible for ongoing operation.
BEFORE YOU START
Good questions. Clear answers.
Who holds the keys?
The custody design specifies that explicitly. Options depend on the operating business, selected providers and required controls; website examples do not decide custody.
Can we use an existing custody provider?
We assess its APIs, signing model, approval features and reconciliation support before defining the integration.
LET’S MAKE THE NEXT STEP USEFUL
Tell us what needs to work better.
Talk with our team
Explore with our AI guide, or reach the people who can scope the work.